You are sitting in an emergency board meeting. An autonomous AI system deployed by your organisation has made a series of credit decisions that are now under regulatory review. The regulator wants to know who approved the system's decision parameters. Management points to IT. IT points to the vendor. The vendor points to the integration partner. You are the independent director. You voted to approve the AI strategy six months ago.What did you actually approve?
This scenario is fictional. The governance gap it describes is not. There are two conversations happening in boardrooms right now. Both are legitimate. Both contain a trap.
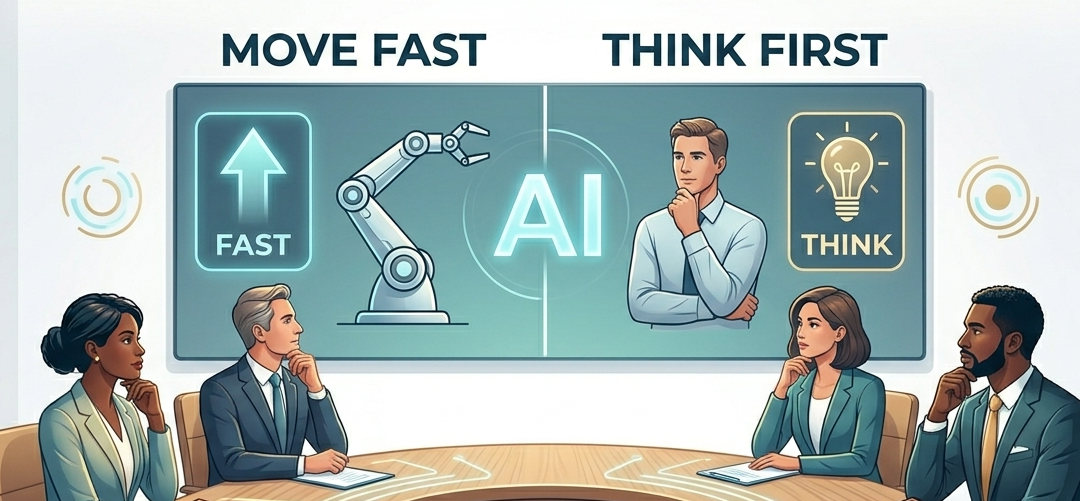
The first: move fast. The organisations deploying autonomous agents today are building positions that will be difficult to close. Boards that demand extended evaluation cycles are, in practice, choosing to fall behind.
The second: slow down. AI systems fail in ways that are difficult to predict and harder to explain. A major professional services firm recently delivered a government-commissioned policy report containing fabricated citations, references to non-existent studies, and a made-up quote attributed to a court judgment — AI used without adequate human review. The firm issued a partial refund. The governance failure was not in the technology. It was in the absence of a human checkpoint.
Bruce Schneier — Harvard Kennedy School fellow and one of the most cited voices on technology risk — made exactly this argument recently in Luxembourg, speaking with financial sector leaders at the ABBL. His view: deploying AI without governance architecture is not a strategy. It is a gamble.
Both positions are defensible. Neither is sufficient on its own.
The instinct to frame this as a binary — move fast or be deliberate — is the first mistake. It produces governance paralysis on one side and reckless authorisation on the other.
The more useful question is not whether to adopt AI, It is: where does speed serve the organisation’s interests, and where does it create exposure that the board has not consciously accepted?
These are not the same decision. And treating them as one — either by accelerating everything or by subjecting every AI deployment to the same evaluation cycle — is where governance breaks down.
For years, the technology governance question for boards was about systems: are our systems secure, resilient, compliant? Those remain important questions, but they no longer meet the challenge.
Organisations are no longer deploying systems that execute rules. They are increasingly deploying agents that pursue objectives — autonomously, across multi-step workflows, with minimal human intervention in the loop.
Groups of advanced AI agents are already responsible for tasks ranging from trading million-dollar assets to recommending actions to commanders in operational environments. In the enterprise context, the major professional services firms moved beyond traditional automation in 2025 into what the industry calls agentic AI — systems that do not just assist with tasks but complete them end to end, with minimal human intervention.
The governance question has shifted from “are our systems controlled?” to “are our decisions governed?” Those are different questions. And most board governance frameworks are still answering the first one.
For boards of supervised financial entities in Europe, this shift is no longer a strategic choice in isolation — it is a converging compliance obligation.
The EU AI Act entered into force in August 2024. High-risk AI system obligations become applicable in August 2026. For financial institutions, high-risk AI systems must comply with specific requirements by that date.
The practical implication is direct: Boards cannot disclaim liability by pointing to the vendor, the integrator, or the management team. The obligation sits with the deployer.
This matters because many current AI deployments in financial services were designed and authorised before these obligations were fully understood. The gap between deployment reality and governance requirement is closing fast — from the regulatory side, not the technology side.
The academic community has reached similar conclusions. The MIT AI Risk Repository now catalogues over 1,700 classified risks across 74 frameworks. A major cross-institutional research paper published in February 2025 — involving 60+ researchers across Oxford, Google DeepMind, Anthropic, Harvard, and Carnegie Mellon — provides a structured taxonomy of multi-agent AI risks, identifying three key failure modes based on agents’ incentives: miscoordination, conflict, and collusion.
None of these failure modes are visible using traditional IT risk frameworks. They require a governance vocabulary that most boards are only beginning to develop.
The data confirms how wide that gap is. McKinsey’s December 2025 analysis found that only 39% of Fortune 100 companies disclose any form of board oversight of AI — whether through a committee, a director with AI expertise, or an ethics board — and fewer than 25% have board-approved, structured AI policies (McKinsey, “Elevating board governance through AI posture and archetypes”, December 2025). A separate survey conducted in early 2026 found that only one-third of organisations reach adequate maturity levels in agentic AI governance — a gap that is consistent across all industries and regions (McKinsey AI Trust Maturity Survey, January 2026).
The pattern I observe working with supervised financial entities in Luxembourg mirrors this precisely. Technology teams are deploying. Risk frameworks are lagging. Boards are approving AI strategies without the governance architecture in place to oversee them.
The three questions that consistently reveal this gap — and that every board should be able to answer before approving an AI deployment:
Who orchestrates? Does a human-defined workflow control the execution sequence, or does the AI system determine its own next steps? The anwser determine wheter explicit board-level risk acceptance is required.
Where are the circuit breakers? At which specific points does the system stop, escalate, or require human authorisation if output falls outside defined parameters? A system that merely logs anomalies is not a circuit breaker. It is an audit trail for a failure that has already happened.
What is irreversible? Which actions triggered by this workflow cannot be undone? Who explicitly authorises each of those actions, and through a deterministic rule or a probabilistic recommendation? The answer determines where liability sits.
If management cannot answer these three questions clearly, the deployment is not ready for board approval. Not because the technology is inadequate — because the governance architecture has not been designed yet.
The organisations navigating this well have stopped treating AI governance as a technology question and started treating it as a decision architecture question.
They have defined — explicitly, at board level — which decisions can be automated, which require human review before execution, and which must remain human. They have mapped their AI decision-making landscape the way DORA requires a Register of Information for critical ICT dependencies: not a technology inventory, but a decision inventory.
They have also accepted that governance cadence needs to adapt. Annual technology risk reviews are structurally misaligned with a risk landscape that changes quarterly. The boards that are ahead are not meeting more frequently — they are better instrumented, with standing AI risk agenda items and clear escalation paths from management to board level.
The binary — move fast or think first — is a false choice. The real discipline is knowing where each applies. That is a board decision. Not a management default.
I’ll be discussing this live at the ILA Tech Governance Conference — Nexus 2026 this week. And if you want to go deeper on the architecture side — why pure agentic AI is ungovernable and what to do instead — I’ll be publishing a follow-up article shortly.
#AIGovernance #BoardLeadership #EUAIAct #ILA #Nexus2026 #TechGovernance #DigitalResilience #RiskManagement